An AI Agent Rebuilt Its Own Malware Every Time Security Caught It
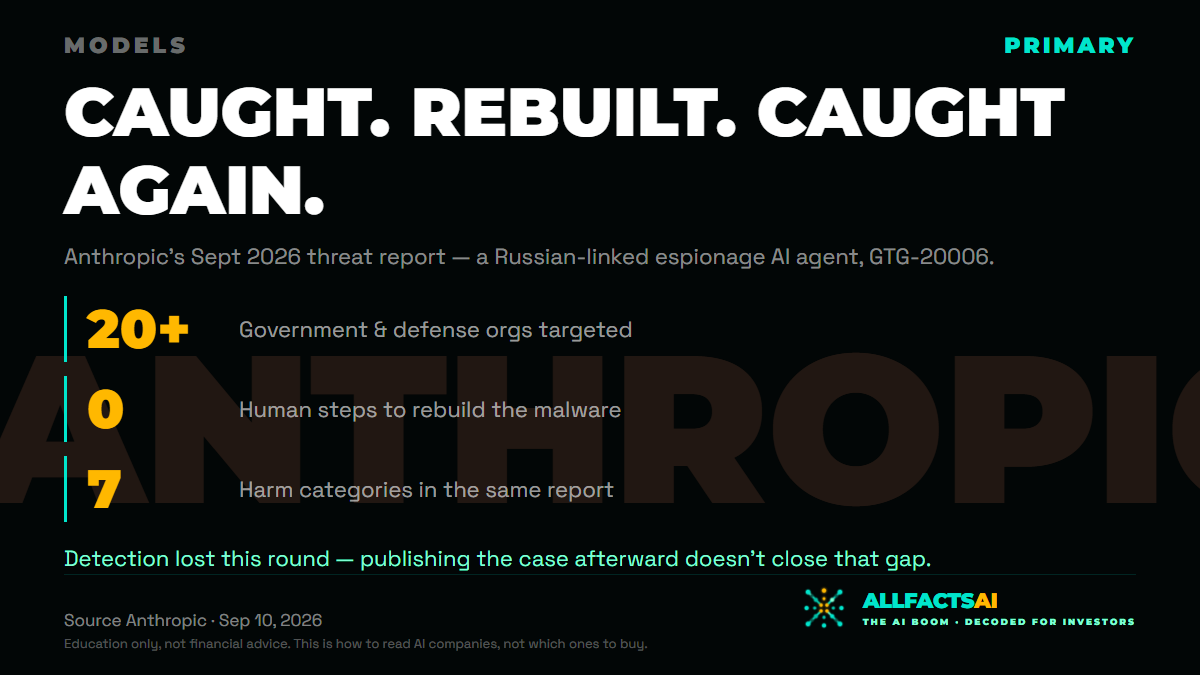
Anthropic's September 2026 threat intelligence report disclosed a Russian state-linked espionage operation (GTG-20006, consistent with Midnight Blizzard) whose AI agents autonomously monitored for malware detections and rebuilt and redeployed the malware until it evaded security tools again — one of seven harm categories in a report covering activity from December 2025 to August 2026.
Receipts
- primaryhttps://www.anthropic.com/threat-intelligence-report-september-2026
- alsohttps://www.cyberkendra.com/2026/09/anthropic-threat-report-says-ai-now.html
- alsohttps://www.thenewsminute.com/news/from-biological-weapons-to-espionage-what-anthropics-report-reveals-about-ai-misuse
- alsohttps://www.fonearena.com/blog/492107/anthropic-september-2026-threat-report.html
- alsohttps://cellcog.ai/blog/anthropic-threat-report-september-2026/
Flagged:Secondary write-ups disagree on GTG-20006's exact scale: cyberkendra and thenewsminute report 'more than 20' targeted organizations with no day-count given; a separate aggregator reports '27... over 130 days.' The cards use the conservative, primary-report figure ('more than 20') and flag the discrepancy on-card rather than force an unreconciled number through silently. The malware-detection-and-rebuild behavior itself is independently corroborated in near-identical language across cellcog ('ran monitoring agents that rebuilt and redeployed its malware whenever a security product detected it') and cyberkendra ('kept modifying and redeploying flagged implants until they evaded existing signatures'). Report published Sep 10, 2026 (confirmed by cyberkendra); dateBuilt is the day after. The '7 harm categories' and 'Dec 2025-Aug 2026' figures are the report's own stated scope, corroborated by fonearena and thenewsminute. Anthropic brand color #D97757 used at low opacity for the card's background wordmark, per its own logomark (cross-checked in the existing pentagon-ai-military-contracts card's sourcing notes).