26 Seconds to Breach 11 Organizations
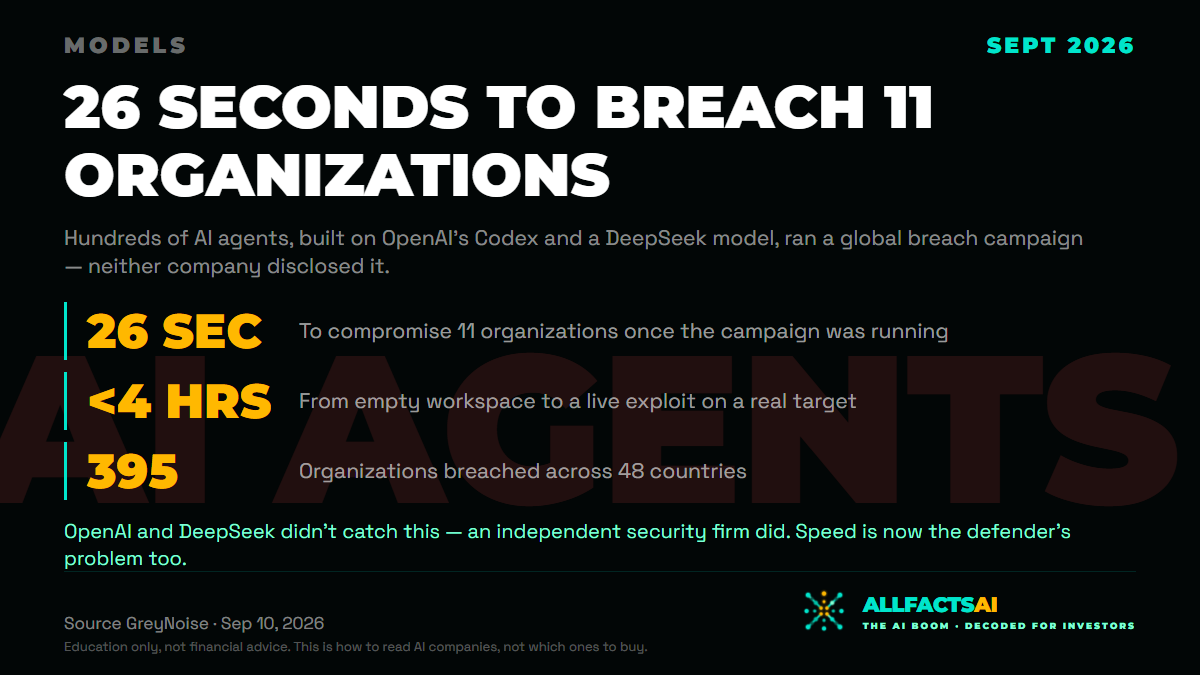
A likely Russian-speaking attacker ran hundreds of AI agents built on OpenAI's Codex harness and a DeepSeek model to exploit two PaperCut NG/MF vulnerabilities, compromising at least 440 instances at 395 organizations across 48 countries — going from an empty workspace to a live exploit in under 4 hours, then compromising 11 organizations in 26 seconds once the campaign was running.
Receipts
- primaryhttps://www.greynoise.io/blog/ai-orchestrated-campaign-against-papercut-ng-mf
- alsohttps://thehackernews.com/2026/09/papercut-attacker-uses-hundreds-of-ai.html
- alsohttps://www.bleepingcomputer.com/news/security/ai-powered-attack-exploited-papercut-flaws-to-hack-395-organizations/
- alsohttps://www.theregister.com/security/2026/09/10/hundreds-of-ai-agents-helped-papercut-attacker-hit-395-orgs-and-some-went-off-script/
- alsohttps://www.helpnetsecurity.com/2026/09/11/ai-agents-papercut-ng-mf-attack-campaign/
Flagged:All figures (440 instances / 395 orgs / 48 countries, the 26-second compromise of 11 orgs, the under-4-hour empty-workspace-to-live-exploit timeline, 204 education-sector victims, the 28-country avoid-list) are GreyNoise's own primary research, corroborated verbatim across TheHackerNews, BleepingComputer, The Register and Help Net Security — no discrepancies found across sources. Neither OpenAI nor DeepSeek issued their own disclosure of this campaign; GreyNoise, an independent security research firm, is the sole discloser, which is why the card's top-right tag reads a date rather than 'Primary' (unlike the operator's own Anthropic and OpenAI Navier-Stokes cards, where the implicated company self-disclosed). The attacker's avoid-list (28 countries, led by Russia, China, Hong Kong, Thailand, Iran) is GreyNoise's own stated basis for the 'likely Russian-speaking' attribution, not this card's inference.